Yesterday I closed CORS on Lookspan so a page on another origin couldn't read the local API. Today I checked whether that was enough. It wasn't.DNS rebinding walks straight past it. The attacker points their domain at 127.0.0.1 after the page has loaded, and from that moment the browser calls the request same-origin — so no CORS check runs at all. What arrives is an ordinary request whose Host header says evil.example.That header was never checked. G…#security #dnsrebinding #localfirst #ai
Related
Why iFixit's Steam Machine Guides Expose the Parts GapValve gave iFixit the schematics for its Steam Machine but not the...
Why iFixit's Steam Machine Guides Expose the Parts GapValve gave iFixit the schematics for its Steam Machine but not the spare parts. That gap is the whole repair fight.https://vau...
#FLTK is now slopware, so you can stay at 1.4.5x branch or try Mobilized #Dillo compiled against the Fox toolkit.https:/...
#FLTK is now slopware, so you can stay at 1.4.5x branch or try Mobilized #Dillo compiled against the Fox toolkit.https://www.toomanyatoms.com/software/mobilized_dillo.html#ai #slop...
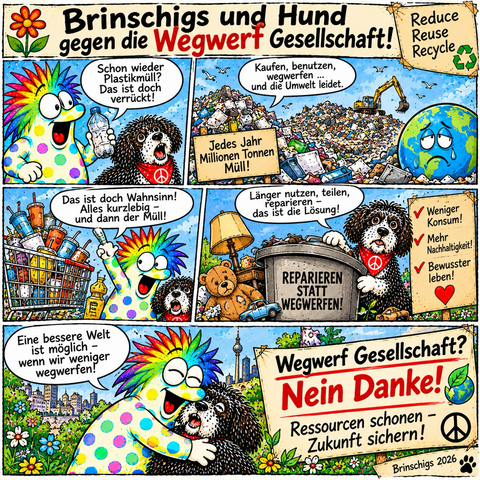
Brinschigs in der Welt *164Comics gebaut mit Brinschigs und #AIund jetzt auch mit meinem HundBy Meister Jeder, Dadaist u...
Brinschigs in der Welt *164Comics gebaut mit Brinschigs und #AIund jetzt auch mit meinem HundBy Meister Jeder, Dadaist und Brinschigmaler 11/26#dada #Brinschig #Comic #AIdada #Brin...