My LLM sandbox environment Umwelt has gotten a really nice addition to - remote containers. You configure remotes that LLMs are allowed to access, and those then show up as "host=" parameters to the commands the LLM already knows about. The remote commands are run inside of containers just as local Umwelt installations.A sysadm-tasked agent can thus be allowed to poke at other machines within well defined capability limits. No risk of injection attacks through log files (yes, this is a vector!) causing an agent to take ... less than optimal actions.I think it's time I put together a video. There are many sandboxes but mine is perfect for me :Phttps://git.sync.wtf/troed/umwelt#LLM #AI #CyberSecAllTheThings
Related
RE: https://social.lansky.name/@hn50/117641046063643892#AI bias.A white person holding a bag of Doritos is classified as...
RE: https://social.lansky.name/@hn50/117641046063643892#AI bias.A white person holding a bag of Doritos is classified as a person consuming tortilla chips.A black person holding a ...
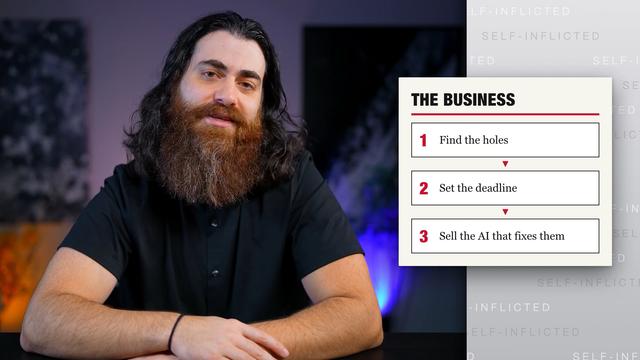
🤔🤔🤔 #AI #Anthropic (Source)
🤔🤔🤔 #AI #Anthropic (Source)
@andiwaffeln I suppose sadly that'd be fitting, given the #Linux #kernel seems to also be aspiring to be filled with #AI...
@andiwaffeln I suppose sadly that'd be fitting, given the #Linux #kernel seems to also be aspiring to be filled with #AI #LLM #code for some reason... 💔 #FreeSoftware #FOSS #FLOSS ...