🤖 CrowdStrike: ARTEX, a Chinese open-source agentic pentest tool, was used with Claude Code to breach South Korean financial firms (Shinhan Bank, Yegaram Savings Bank) in late Sept–early Oct 2026. Claude Code session logs and ARTEX configs were found exposed on a Hong Kong IP. ARTEX is now closed source.🔗 https://thehackernews.com/2026/10/artex-ai-pentesting-tool-used-in-data.html#CyberSec #ThreatIntel #DataBreach #AI
Related
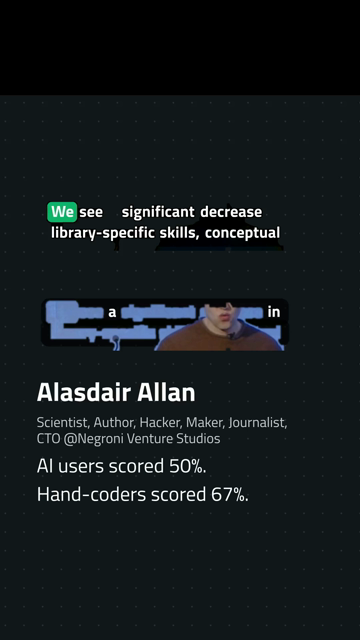
AI makes you faster at writing code. But does it make you worse at debugging it?An Anthropic study tested developers lea...
AI makes you faster at writing code. But does it make you worse at debugging it?An Anthropic study tested developers learning a new library:• AI-assisted coders: 50%• Coding by han...
How to Expand Any Image for FREE! 🤯 AI Uncrop Trick (No Photoshop) https://www.youtube.com/watch?v=XQyWB1utu4o 🎨📐 #Image...
How to Expand Any Image for FREE! 🤯 AI Uncrop Trick (No Photoshop) https://www.youtube.com/watch?v=XQyWB1utu4o 🎨📐 #Image #Expand #AI #Tips #Uncrop
Okay...so what's the opinion of Geoffrey Hinton (2024 Physics Nobel Prize and "The godfather of AI")? (Sadly I saw this ...
Okay...so what's the opinion of Geoffrey Hinton (2024 Physics Nobel Prize and "The godfather of AI")? (Sadly I saw this after Halloween)https://www.youtube.com/watch?v=l6ZcFa8pybE#...